On this page
Key points
- Bandwidth is only one limitPPS, queues, CPU and state can fail before Gbps are full.
- Impact spreadsOne attacked customer can degrade a rack, VLAN or whole platform.
- Mitigate upstreamFiltering too close to the server lets saturation propagate.
The problem: the attack overflows the target
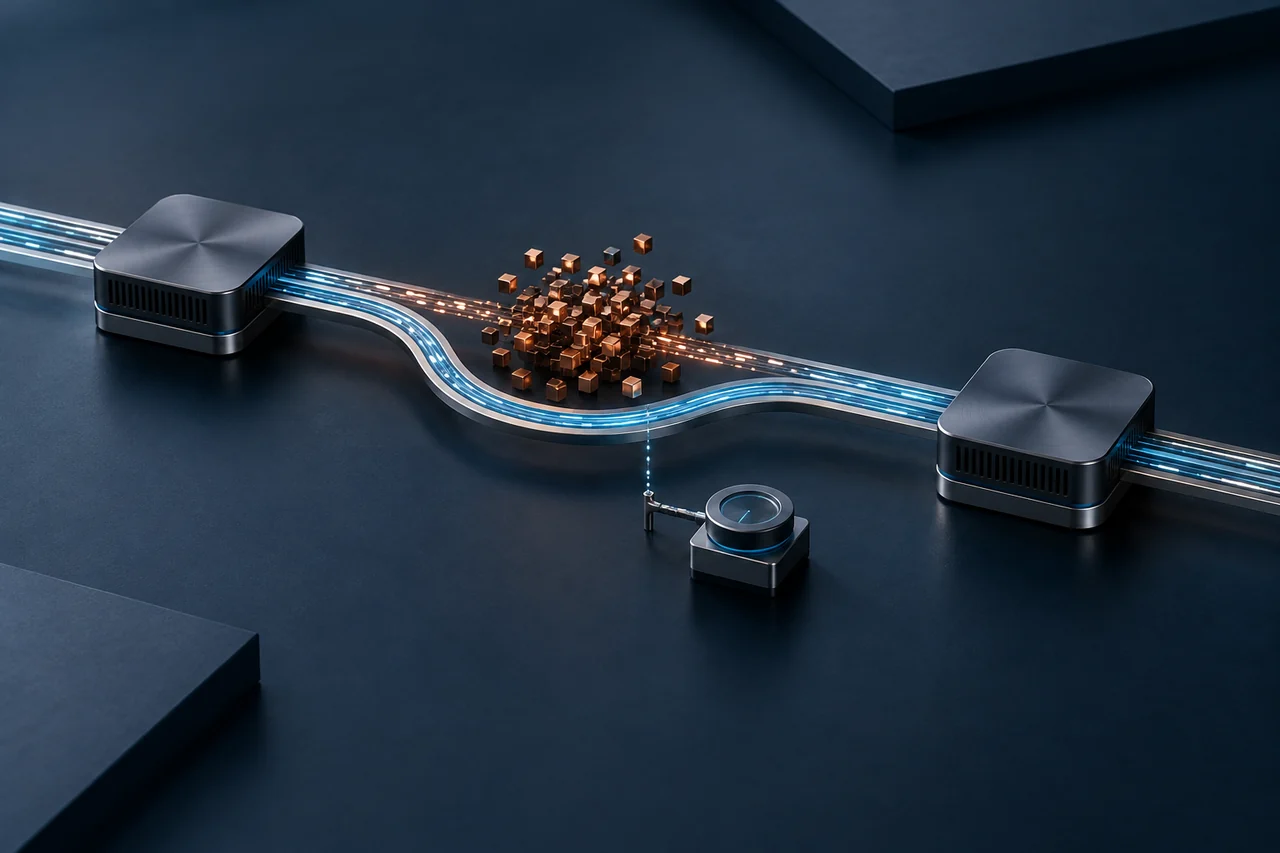
A DDoS attack often targets one IP or service, but the packets cross shared equipment before reaching it. If saturation happens on the upstream link, router, firewall, switch or tunnel, the impact spreads to other services. The targeted server is not always the first component to fail.
Many offers describe only server protection. In reality the incident is decided in the network: port capacity, PPS handled, buffers, state tables, ACLs, return paths and the ability to isolate the affected customer.
Why this is critical for providers and enterprises
For a hosting provider, one exposed customer can create packet loss for others when filtering happens too late. For an enterprise, an attack on a public application can disturb VPN, APIs, telephony, monitoring or administration. For gaming communities, one attacked server can degrade several machines if they share the same link.
The network impact is also financial. Every minute of instability generates support, refunds, emergency migrations and loss of trust. A strong Anti-DDoS architecture reduces this contagion by absorbing or reducing the attack before it reaches sensitive zones.
Possible solutions to contain the impact
The first solution is upstream filtering: protected transit, scrubbing center, FlowSpec or relief rules that avoid filling the customer link. The second is segmentation: separate customers, services and return paths so an attack on one IP does not affect the full platform.
The third is clean traffic delivery through tunnel, cross-connect, BGP or proxy depending on the context. For gaming, a reverse proxy can isolate selected surfaces. For networks and hosting providers, protected IP transit addresses the problem higher in the chain.
Example: hosting provider with several customers on one uplink
A hosting provider runs several dedicated servers behind an uplink. One customer receives a strong UDP flood. If protection happens only on the server, the uplink is already full and other customers see loss. Support then receives tickets from customers who were not directly attacked.
With a cleaner model, traffic is attracted or filtered upstream and only acceptable traffic is delivered back. The attacked customer remains isolated, production capacity stays available and neighbouring customers do not suffer the incident.
Common mistakes
The first mistake is assuming a firewall is enough. A firewall can be excellent for security policy, but it may become the saturation point when it receives too many packets or sessions. The second mistake is looking only at Gbps: high PPS attacks can break equipment without filling the full bandwidth.
The third mistake is not preparing return paths. Blocking the attack is not enough if clean traffic returns through an unstable, undersized or hard-to-debug tunnel. Finally, putting all customers on the same shared paths without isolation makes every incident more dangerous.
FAQ
Common questions on this topic.
Can a DDoS affect customers that are not targeted?
Yes, if it saturates a shared link, router, firewall or path.
Why is PPS important for the network?
Because equipment can fail on packet rate before bandwidth is full.
Does a firewall protect against large DDoS attacks?
Not always. It can become the saturation point if traffic arrives too hard.
How do you avoid the domino effect?
Filter upstream, segment paths and deliver clean traffic over properly sized links.