On this page
Key points
- Pre-filtering should relieve early pressure without over-decidingIts best role is to remove obvious noise, protect transit and prepare cleaner traffic for finer decision layers.
- It should not make every decision aloneThe more brutal the upstream rule is, the more false-positive risk grows.
- It improves global cost/performanceBy removing obvious noise early, it makes specialised filtering more stable and more efficient.
When upstream pre-filtering becomes essential
It becomes essential as soon as an attack can damage the network path before your fine-grained logic even gets a chance to act. This is typically the case when the link, buffers, packet rate or simple traffic density threaten the stability of the mitigation chain.
Below a certain threshold you can sometimes do everything in one place. Once volume grows, however, the right answer is no longer to keep adding more intelligence at the same point. The architecture first needs breathing room.
- Link protection
- The first benefit is preventing massive traffic from reaching production or the filtering server without relief.
- PPS protection
- Traffic that does not look huge in Gbps can still be destructive because of packet rate.
- Economic protection
- Good coarse reduction avoids spending costly cycles on traffic that is obviously useless.
What upstream pre-filtering does well, and what it should not be forced to do
It does very well at coarse sorting based on signals that are robust enough: clearly abnormal packet profiles, repetitive patterns, volumetric signatures or short-lived relief rules. Its job is to reduce pressure and prepare a cleaner stream for the next layer.
What it should not be forced to do is solve every ambiguity of legitimate traffic on its own. The more an upstream layer tries to be “smart” without enough context, the more dangerous it becomes. The correct role is fast, careful and temporary where needed.
- Yes: volumetric coarse reduction, very obvious signatures and short-lived rules.
- Yes: removing upstream patterns that waste the filtering server’s budget.
- No: fine application logic without enough visibility.
- No: broad permanent rules on a service that changes frequently.
What should be filtered upstream in a clean strategy
A clean strategy filters upstream what is stable enough to be handled early without damaging legitimate traffic: some size profiles, protocol or port patterns, volumetric behaviours or floods that are clearly out of profile.
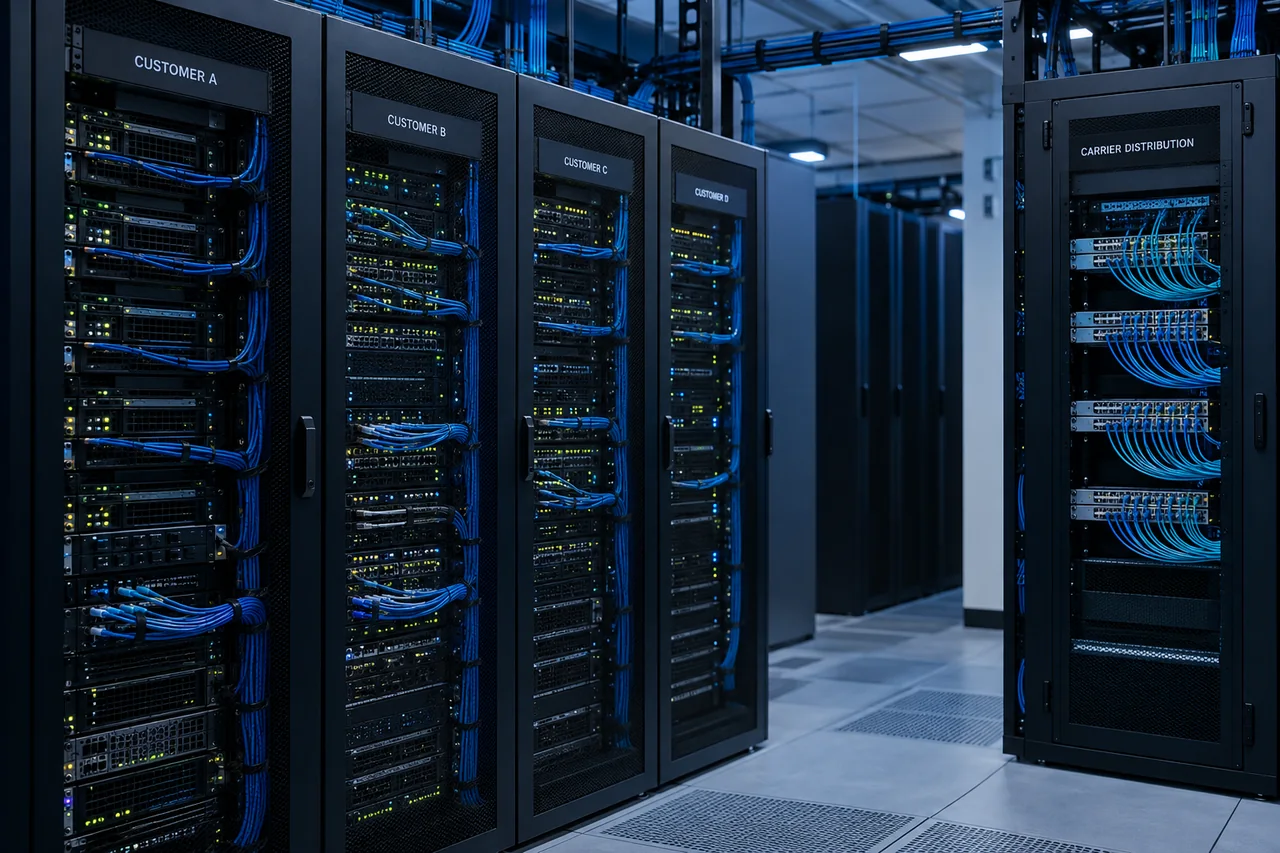
This layer can take several forms: upstream relief at a carrier, short-lived coarse reduction rules, or pre-cleaning before a dedicated filtering server performs more precise work.
Identify the dominant pressure
Link, PPS or CPU cost: know what fails first.
Define robust criteria
Only use upstream signals that are safe enough not to hurt legitimate users.
Keep rules short and revisable
Pre-filtering should follow the attack, not become permanent debt.
What must stay behind it: dedicated filtering, observation and smarter logic
Pre-filtering is only the first barrier. Behind it, you still need a layer that can observe, compare against normal traffic, apply finer signatures and prepare a clean handoff back to the target.
That is exactly where a dedicated filtering server or custom XDP / DPDK / proxy logic makes sense. Upstream relief reduces pressure, the dedicated layer decides more precisely, and production receives traffic that stays usable.
Common mistakes
The classic mistake is trying to do everything upstream. It looks reassuring on slides, but it quickly raises false-positive risk and removes the flexibility you need when a service evolves.
The opposite mistake is to do no relief at all and expect one server or one software stack to absorb massive pressure cleanly. A serious strategy accepts that not every layer has the same role.
- Rules that are too broad
- An upstream rule that is too aggressive can hurt faster than the attack itself.
- Rules that live too long
- What helped on one flood can become harmful the next day.
- No baseline
- Without visibility into normal traffic, you may end up relieving against your own customers.
FAQ
Is upstream Anti-DDoS pre-filtering enough on its own?
No. It is extremely useful for coarse reduction, but it must remain part of a layered strategy.
Should it always be enabled?
Not necessarily. Its value rises mainly when volume, packet rate or network pressure become a real risk.
Can it work with custom XDP logic or a proxy behind it?
Yes. That is often one of the best setups: upstream removes obvious noise and the custom logic finishes the job.
What is the biggest danger?
Using rules that are too broad, live too long or are not correlated to legitimate traffic.
What should good upstream pre-filtering actually do?
Relieve early, protect links and prepare the fine decision layer. It should not try to decide everything with fragile complexity.