Peeryx Network Anti-DDoS technology
Anti-DDoS technology built for production networks
Peeryx Network protects prefixes, game servers, websites, applications and critical infrastructure by combining upstream capacity, high-performance local filtering and behavioral awareness of legitimate traffic.
AS213382
Independently announced network
Marseille
Infrastructure in service
DPDK · FlowSpec
High-performance filtering
BGP · GRE · VXLAN
Architecture-aware delivery
On this page
Technical figures with a clear source
Peeryx telemetry for observed measurements and capacity available through our transit providers for upstream absorption.
Peeryx telemetry for the stated period. A dash means no publishable measurement. These figures are not an independent software benchmark.
Measurement period : →
View the measurement method →Operational mitigation path
-
Observe
Establish legitimate traffic baselines and service-specific thresholds.
-
Detect
Correlate changes in bandwidth, packet rate, protocols and destinations.
-
Absorb
Offload volumetric attacks through upstream capacity and targeted BGP FlowSpec rules.
-
Filter
Apply L3/L4 processing on the DPDK data plane with service-specific profiles.
-
Deliver
Forward accepted traffic through the agreed handoff without changing the production architecture.
Filtering architecture and capabilities
Each design choice is explained through its role, implementation and impact on protected traffic.
Upstream mitigation architecture
Filtering before customer infrastructure
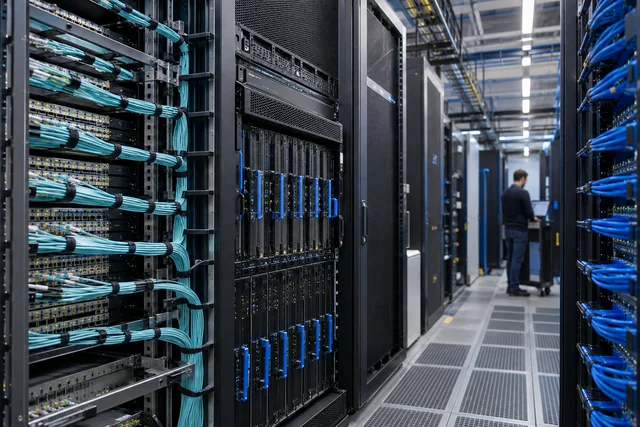
Peeryx Network places filtering servers at the network edge, on points of presence designed to receive traffic before it reaches the protected infrastructure. Traffic crosses the mitigation layer in bridge mode, which enables filtering without imposing heavy application logic or unnecessary complexity on the customer side.
This model protects many use cases: protected IP transit, BGP prefixes, GRE/IPIP/VXLAN tunnels, gaming reverse proxy, dedicated servers and sensitive infrastructure.
- Filtering before customer infrastructure
- Clean handoff for legitimate traffic
- BGP, tunnel and cross-connect compatible
High-PPS DPDK processing
Capacity validated on the deployed hardware
Peeryx uses DPDK-based packet processing in its mitigation architecture. Performance depends on the deployed software, enabled rules, packet sizes and traffic distribution.
CPU, NIC, PCIe bandwidth, NUMA placement and receive queues all constrain forwarding. A port speed or a processor core count does not establish a server’s filtering capacity. Validate Gbps and Mpps together with representative packets, legitimate traffic, enabled features and an explicit packet-loss limit. Historical network telemetry is not a reproducible per-server benchmark.
- Capacity validated on the deployed hardware
- DPDK, RSS and multi-core processing
- Built for high-PPS floods, not only Gbps
Service-aware filtering
Normal-traffic baseline
Overly generic Anti-DDoS filtering can block players, break real-time applications or disrupt business protocols. Peeryx uses behavioral analysis: used ports, protocols, usual volumes, packet sizes, destinations and normal service variations.
When an attack starts, mitigation compares incoming traffic with the expected behavior. Rules are adjusted to block enough of the attack while preserving useful traffic, even when the attacker tries to imitate part of the legitimate traffic.
- Normal-traffic baseline
- Reduced false positives
- Rules adapted to the service actually being protected
Distributed upstream capacity
Multi-transit architecture
Peeryx combines upstream transit and local filtering. Resilience depends on independent, working paths and on the capacity remaining after a failure; planned points of presence are not additional live capacity.
The announced 15 Tbps+ refers to capacity available through upstream providers. It is shared network capacity, not a dedicated customer reservation or a measure of locally owned filtering. Customer port limits, the clean handoff and upstream mitigation policies still apply.
- Multi-transit architecture
- Shared upstream capacity, separate from local filtering
- Goal: reduce the attack without intentionally cutting the IP
Targeted BGP FlowSpec mitigation
Attack detection
When an attack is detected, Peeryx can automatically generate BGP FlowSpec rules that target the observed characteristics: protocol, ports, TCP flags, packet lengths or impacted destinations.
A FlowSpec instruction takes effect only if the receiving provider accepts it and the forwarding equipment installs a supported action. Validate the match against legitimate traffic, observe its effect and define withdrawal conditions. An established BGP session alone does not prove that filtering is active.
- Attack detection
- Selective rule generation
- Upstream reduction followed by local cleaning
Marseille network presence
Measure latency on the actual service path
Marseille is the currently declared operational location. Confirm the delivery point and available connectivity for your service before planning a deployment.
Latency follows the actual forward and return paths, peering and congestion. Measure it from your users and origin, during normal operation and mitigation; geographical proximity alone does not establish a latency guarantee.
- Measure latency on the actual service path
- Strategic position toward the Mediterranean region
- Delivery designed for network stability
Gaming and real-time profiles
FiveM and Minecraft Java: see the dedicated offers
The public reverse-proxy offers cover FiveM and Minecraft Java. Supported versions, origin delivery, exposed ports and any administration or web endpoints must be reviewed for the selected service.
Network filtering and protocol-specific modules have different scopes. Other games or applications require a compatibility review; the presence of a module in the filtering catalogue does not mean it is enabled or included in every offer. No generic L7 or universal anti-bot result is implied.
- FiveM and Minecraft Java: see the dedicated offers
- Adapted UDP/TCP protection
- Priority on game continuity and stability
Post-mitigation controls
Block unused ports
After automatic mitigation, Peeryx can apply a post-filtering firewall layer. It can block unused ports, limit specific flows, protect administration services or adapt rules to the constraints of a precise infrastructure.
This layer strengthens security without replacing mitigation: it acts after traffic has already been cleaned by the Anti-DDoS protection.
- Block unused ports
- Restrict sensitive flows
- Customize protection to your architecture
Continuity for legitimate traffic
Low latency
The best Anti-DDoS protection is the one end users do not notice. Peeryx aims to preserve low latency, fewer false positives, network stability and service continuity even during attacks.
The technology analyzes, adjusts and protects in real time. It is not just a capacity promise; it is designed to deliver traffic that is actually usable.
- Low latency
- Network stability
- Service continuity during mitigation
Peeryx Network
Want to validate your Anti-DDoS scenario?
Tell us about your prefixes, ports, games, applications, tunnels or BGP constraints. We will propose a clear architecture adapted to your real use case.
Technical guides
Plan your deployment.
Routing, tunnels and diagnostics: practical explanations to support your technical decisions.